GriffGuard Bridge
A Linux edge architecture combining TLS routing, a web endpoint and managed network services.
Status: Sanitized deployment reference
Tools: Ubuntu · HAProxy · Nginx · Docker · Xray
One public edge, distinct services
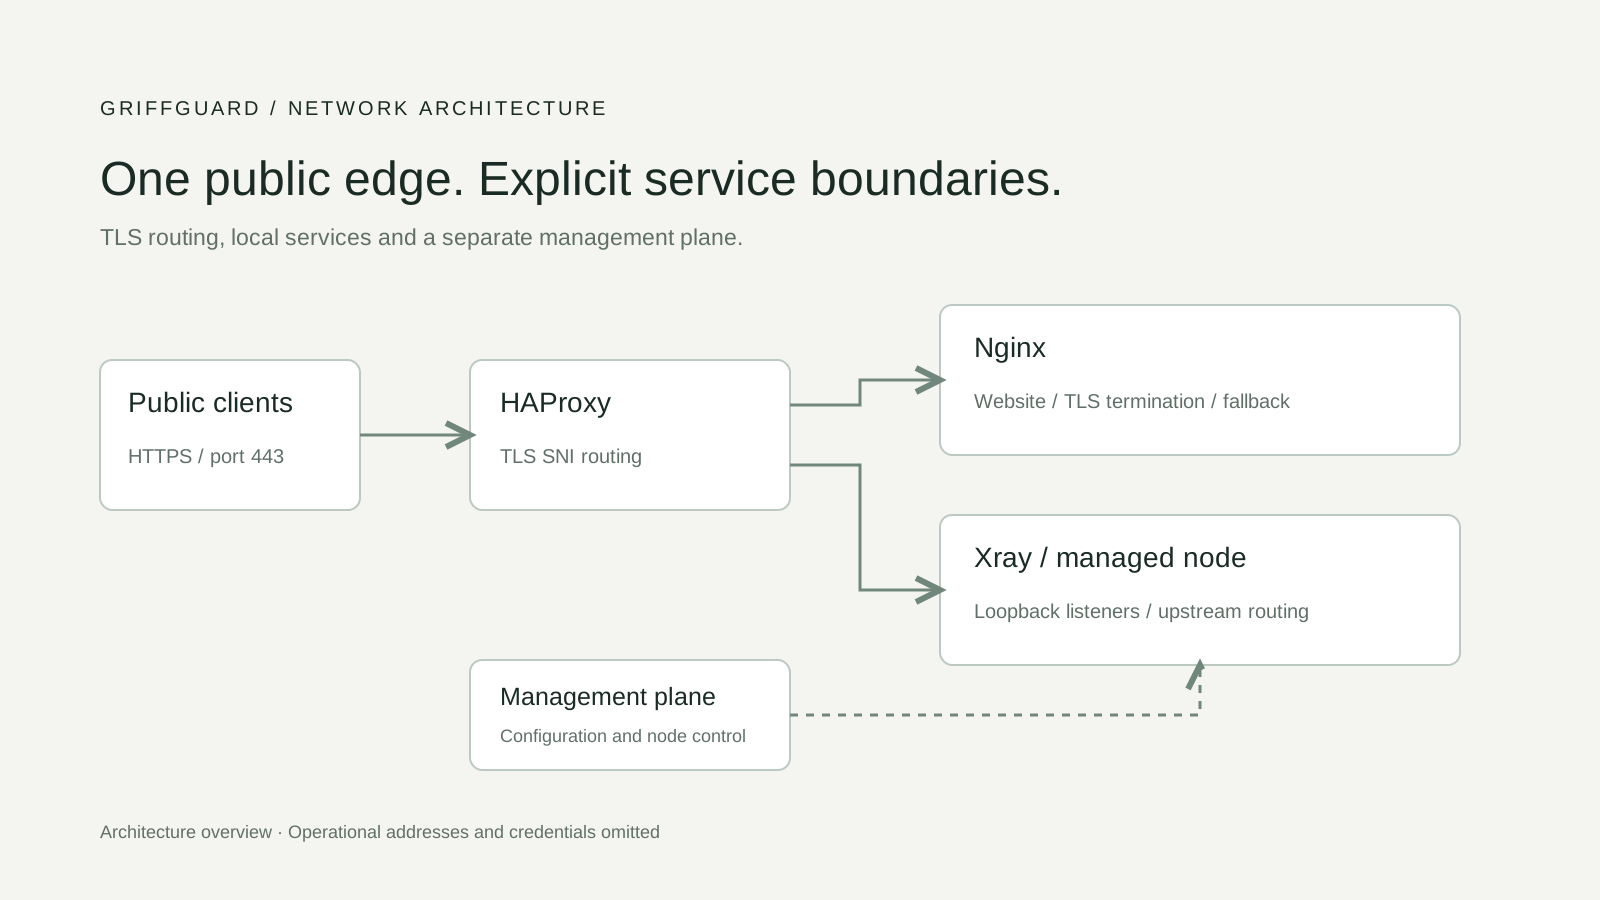
HAProxy owns the TLS entry point and routes connections by SNI. Nginx serves the web endpoint and terminates selected TLS paths, while application services use loopback interfaces where possible.
Deployment in explicit stages
Host preparation, installation, edge activation and verification are split into auditable steps. Bootstrap configuration is separate from centrally managed runtime configuration.
What the portfolio shows
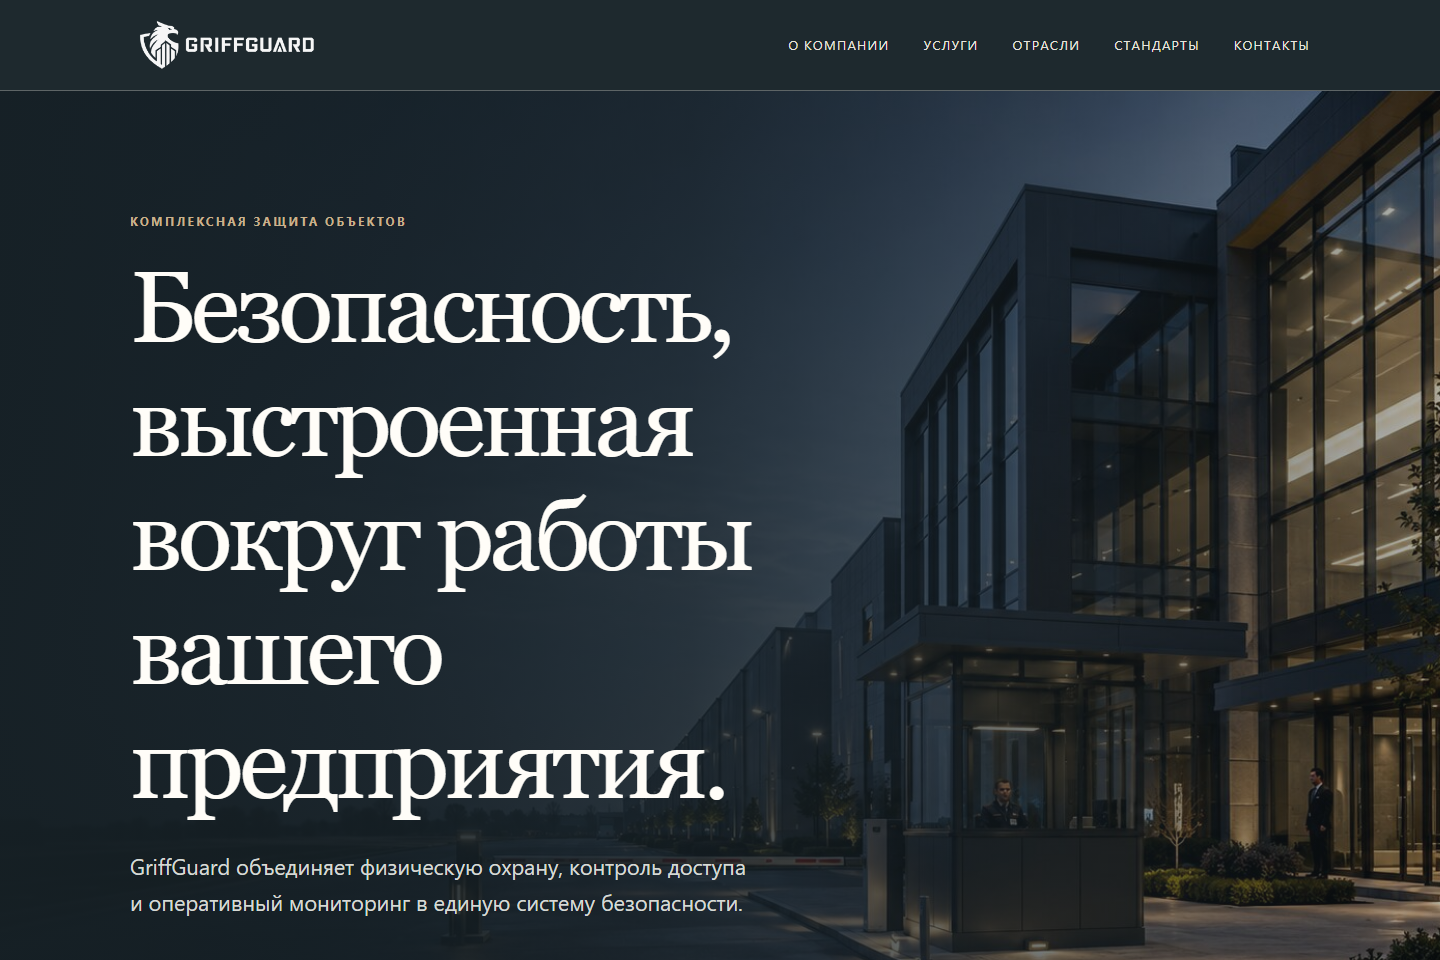
The supplied reference contains sanitized routing examples, scripts and a static web endpoint. The diagram shows architecture; the screenshot shows that endpoint, not a monitoring dashboard. Operational keys, certificates and credentials are excluded.
Project views
Architecture reference and supplied public web endpoint.